

Governance Contracts
Governance contracts are essential for secure, flexible, and upgradeable management of Euler Vault Kit (EVK) vaults and oracle routers. They enable fine-grained control over vault operations, risk parameters, and emergency responses, balancing the need for rapid intervention with robust user protection.
Key Principles
Governance contracts in Euler are designed for security and flexibility, but their deployment and management require careful attention. Governance contracts are deployed from existing, audited factories, as described below. The Toolbox manages the vaults and routers that sit under them: Market Ops reads which contract governs each component, offers the ways in that a governor contract exposes (the admin timelock, the wildcard timelock, the cap risk steward) and lets the operator choose, hands transactions to a Safe, and schedules them on a timelock. Tools → Governance deploys a governor suite (the governor contract with its admin and wildcard timelocks) from Euler's factory, an optional cap risk steward, and later role changes through the admin timelock. See Governance: governors, timelocks, Safes. Teams that manage large clusters from code can use euler-vault-scripts.
To ensure consistent and secure governance across all protocol components, governor contracts should be installed not only on vaults but also on the oracle router. This approach provides fine-grained control and robust protection for both lending markets and their associated price feeds.
Recommended Architecture
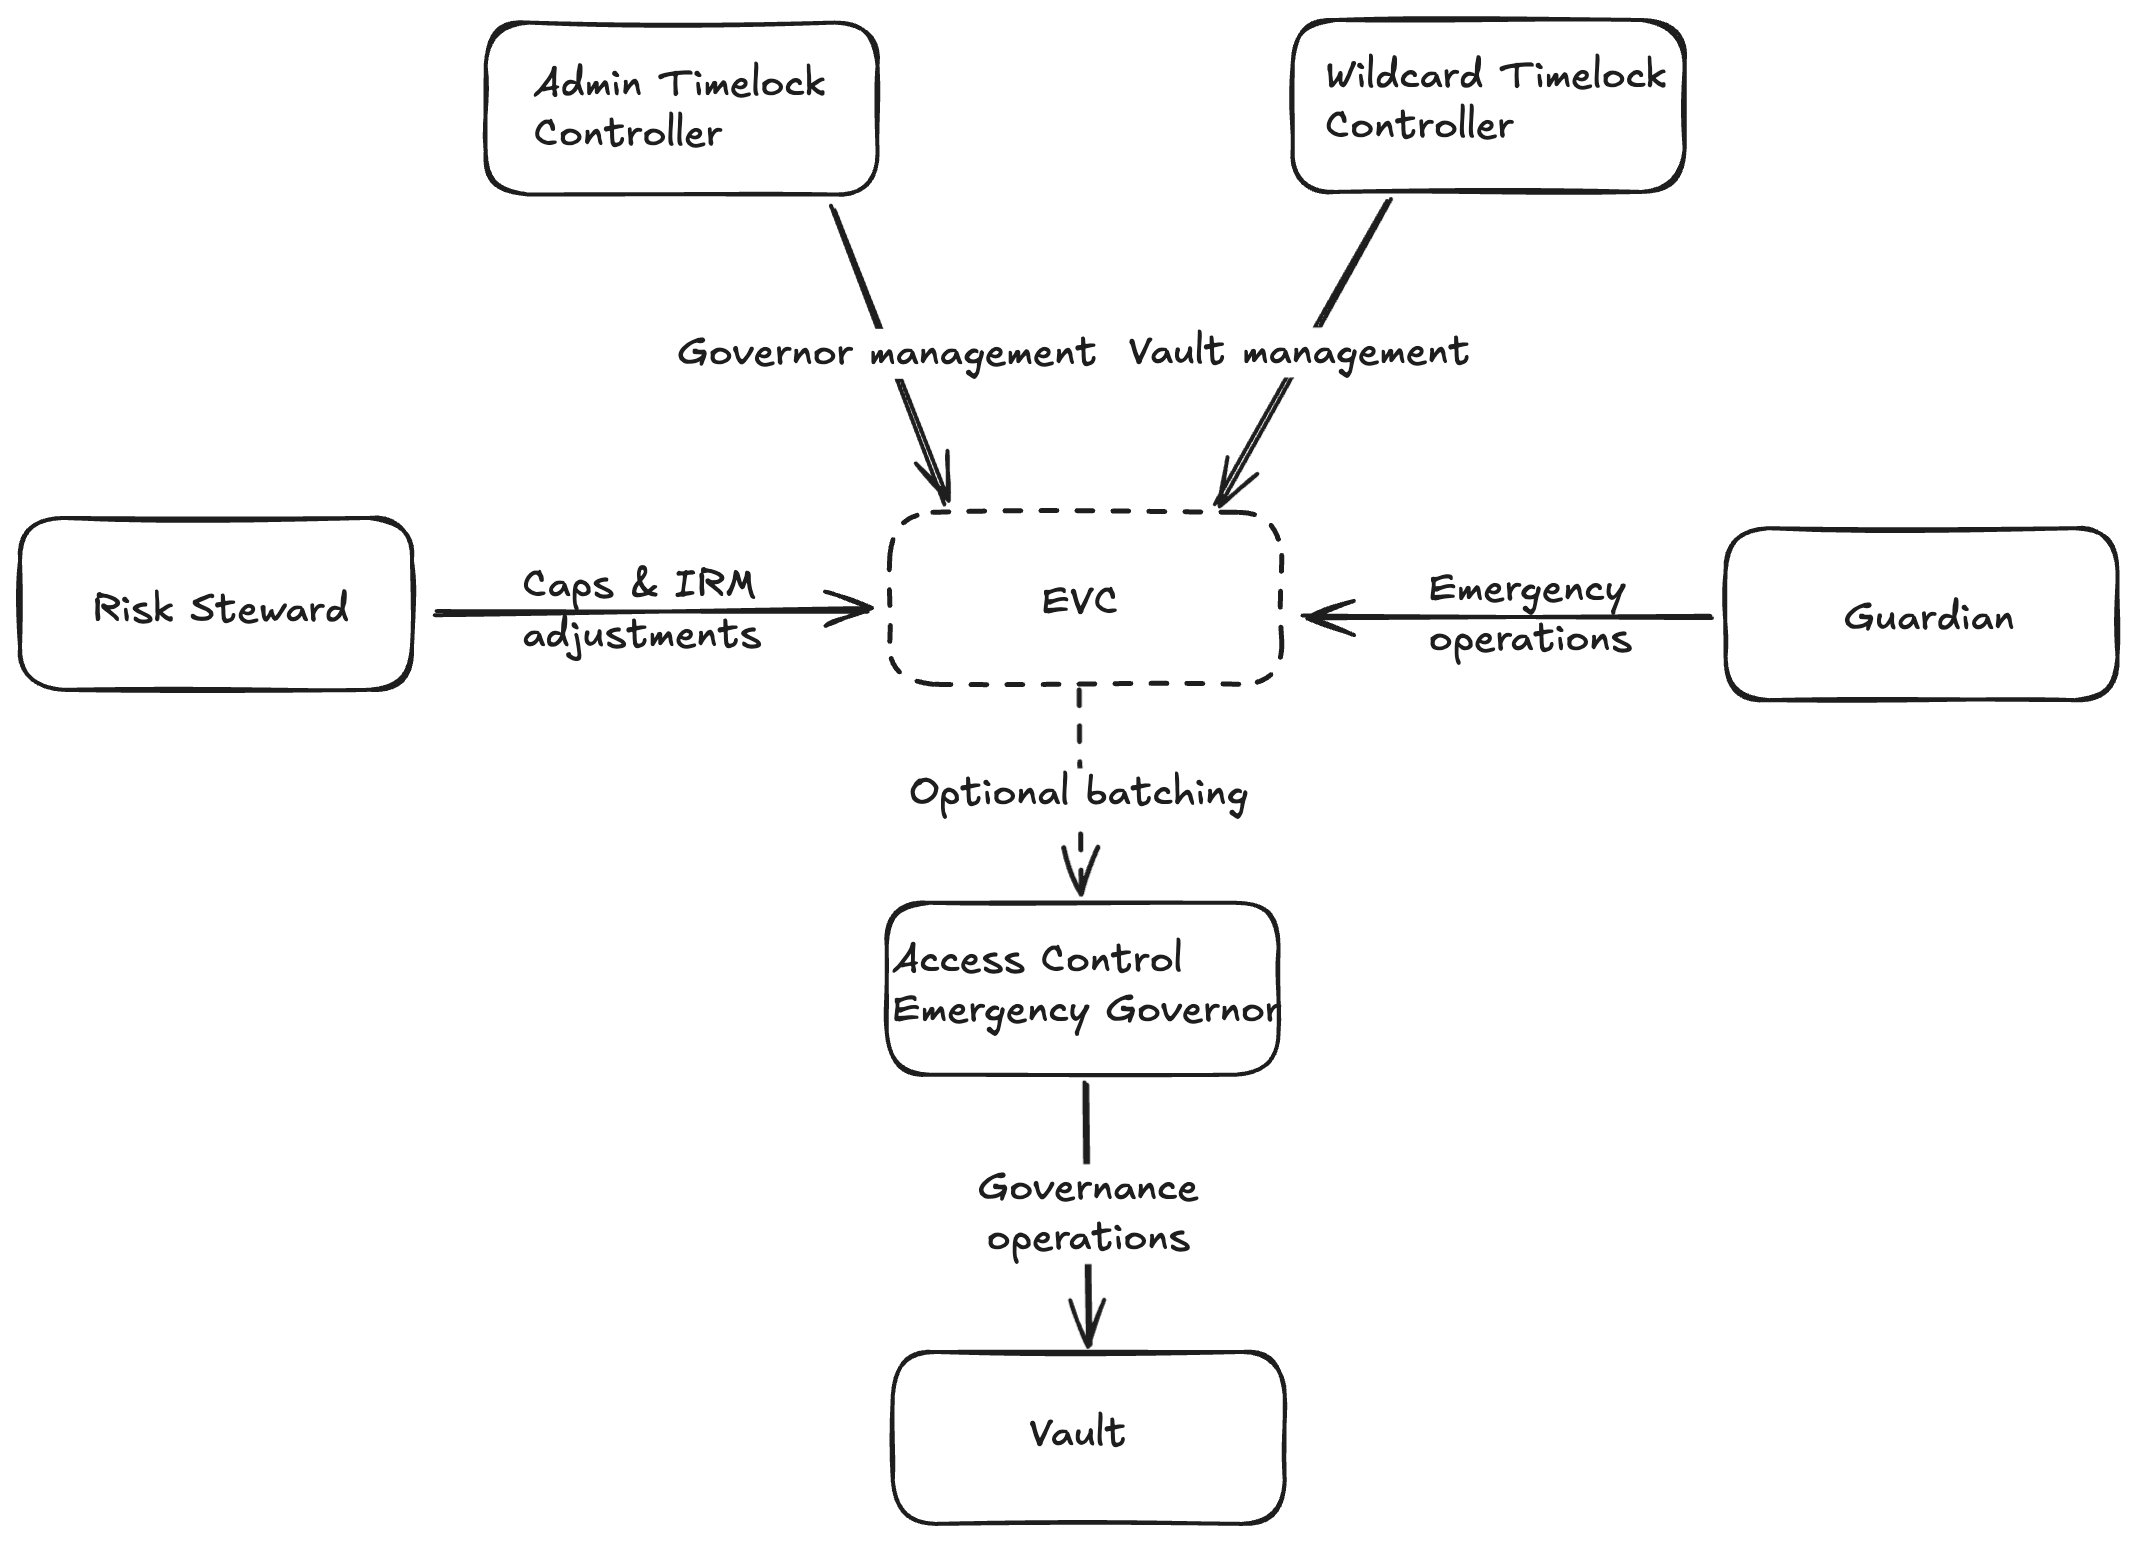
The recommended governance suite is illustrated below. It features dual timelocks (admin and wildcard), a risk steward, guardian, and emergency roles, all allowing for the operations to be (optionally) batched via the EVC. This architecture enables:
- Time-delayed governance for transparency and user protection
- Emergency response capabilities for rapid risk mitigation
- Role separation for operational and administrative security
Components
GovernorAccessControlEmergency: Selector-based access control contracts for fine-grained permissioning and emergency actions.CapRiskSteward: Specialized risk management contract that allows authorized users to adjust supply and borrow caps within predefined safety limits and cooldowns, and to update interest rate models (IRMs) only to those deployed by a recognized factory.GovernorAccessControlEmergencyFactory: Factory for deploying the full governance suite, including timelocks and emergency roles.CapRiskStewardFactory: Factory for deploying CapRiskSteward contracts that work alongside selector-based governors for delegated, but limited, risk management that can bypass timelock controllers.
Deployment & Management
Deployment Process
-
Prepare timelock parameters:
- Set
minDelay(minimum 1 day) for both admin and wildcard timelocks - Define proposers, cancellers, and executors for each timelock
- Identify emergency guardians for rapid response capabilities
- Set
-
Deploy through
GovernorAccessControlEmergencyFactory:- Call
deploywith the prepared parameters - Record the addresses of deployed contracts
- Call
-
Install governance:
- Set the
GovernorAccessControlEmergencyas governor for your vault(s) - Install the same governor on your oracle router
- If using
CapRiskStewardfor delegated risk management:- Deploy
CapRiskStewardviaCapRiskStewardFactory, providing the governor access control contract, IRM factory addresses and the admin address - Grant
setInterestRateModel.selectorandsetCaps.selectorroles to theCapRiskStewardon the governor contract - Assign the wildcard role on the
CapRiskStewardto a multisig or other trusted address
- Deploy
- Set the